Forging Cyber Resilience Via Steady Compliance And Security Controls Validation

Instead of scrambling before an audit to gather evidence of annual pentests and such, organizations can leverage ASV reports which repeatedly reveal compliance. Overall, ASV offers steady, proactive audits from an attacker’s perspective, ensuring security controls adapt as cloud providers evolve. For instance, ASV helped a financial establishment uncover an unsecured connection between a developer’s cloud surroundings and the company network, stopping potential assaults.
- It is the proactive, empirical, and ongoing means of rigorously testing and validating the true effectiveness of an organisation’s security controls in opposition to the backdrop of realistic, contemporary cyber threats.
- The combination of each BAS and APT in a safety program supplies a complete, proactive method to threat detection, vulnerability management, and danger reduction, each addressing particular needs within the safety lifecycle.
- Deep, point-in-time expert analysis suited for complex eventualities, audits or regulatory wants.
- Enterprises in regulated industries (finance, healthcare, utilities…) can use ASV to maintain steady compliance with security testing requirements.
- In an ongoing process, steady testing and validation supports the adaptability of your defenses, guaranteeing they’re always up to the challenge to defend against today’s most sophisticated threats.
> What To Expect From A Bas Tool
This is the place BAS, a core know-how in Adversarial Publicity Validation, modifications the game. BAS doesn’t simply highlight vulnerabilities; it validates their exploitability in context. A framework of safety necessities for designing, developing and testing modern net applications and web companies.
Ot / Ics Cybersecurity
Organizations make investments closely in safety tools and response groups but rarely are able to validate whether those controls really work collectively under real-world assault circumstances. At Validato, we assert that these two pillars – Steady Compliance and Safety Controls Validation – are not simply complementary, but inextricably and mutually beneficially linked. True, sustainable continuous compliance in today’s refined threat panorama is simply unattainable with out the dynamic, evidence-based insights furnished by steady Security Controls Validation. Conversely, a robust compliance framework supplies the strategic path and impetus for more targeted and efficient validation efforts. By addressing vulnerabilities throughout these important vectors, firms can develop a robust security technique that covers all bases. Let’s take the example of outlets, who should defend each their online platforms and in-store methods https://eurodialogue.org/nato/Smart-defence-or-optimisation-of-security-according-to-NATO, thereby ensuring a secure shopping environment for their customers.
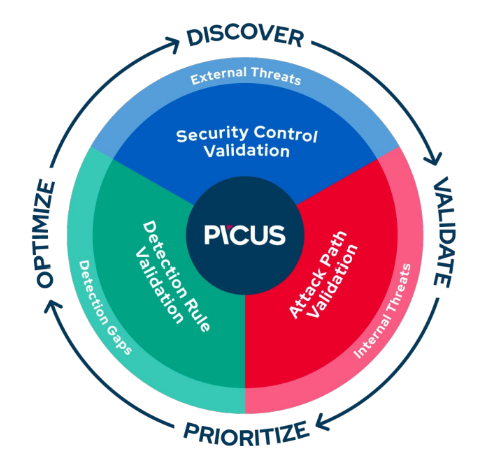
Risk Exposure Administration And Threat Discount With Picus Platform

This validation permits focused risk discount, informed investment selections, and compliance with stringent regulatory necessities. As threats and enterprise environments evolve, security control validation will stay at the forefront of protection, supporting both operational readiness and strategic governance for cybersecurity leaders. Safety management validation is the method of proving that an organization’s prevention, detection, and response security controls work effectively against real-world cyber attack strategies. Security management validation is best when performed continuously.
Trying Forward With Continuous Security Validation
By activating actual response processes throughout controlled assault simulations, this validation demonstrates whether or not teams can determine, comprise, and remediate threats within outlined service levels and cut back mean time to reply (MTTR). OnDefend validates your organization’s capability to forestall, detect, and reply to real-world cyber assaults. Via controlled emulation of recent threat actor ways, we expose weaknesses throughout your security stack, measure the effectiveness of your defenses, and empower your teams with where to begin.
Similarly, for cyber insurance or board reporting, ASV provides actionable, data-driven metrics that provide unparalleled visibility into your security performance. ASV acts as an automated QA system, repeatedly validating security and enhancing SOC effectivity. For Safety Operations Centers (SOCs), Automated Safety Validation boosts detection, reduces alert fatigue, and streamlines incident response. Extremely automated and repeatable, ensuring consistent quality and efficiency in identifying vulnerabilities. Detects potential vulnerabilities but cannot affirm real exploitability or business influence.
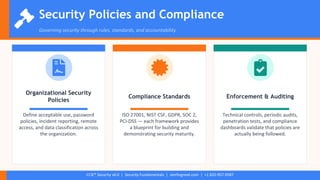
That’s why proactive security validation is so crucial, making sure your defenses are always ready, and adapting in real-time to no matter comes your way. Security management validation is the practice of testing whether preventive, detective, and response controls actually work under practical assault conditions. In follow, it helps organisations confirm coverage, find drift, and confirm that controls nonetheless cut back threat as threats, methods, and configurations change. Security control validation is underpinned by a quantity of core concepts that reinforce its strategic and operational importance. These ideas are essential for aligning technical safety controls with enterprise danger management targets and regulatory obligations. Security control validation helps frameworks such as SOC 2, ISO 27001, NIST, HIPAA, and PCI DSS by demonstrating that security controls usually are not solely current but efficient in real-world assault eventualities.
Validation offers defensible proof that controls operate as supposed past guidelines compliance. Organizations might validate safety controls quarterly or after main incidents, software changes, or architectural updates. Nonetheless, steady security management validation offers the very best degree of assurance by figuring out control failures as soon as they’re launched somewhat than months later.
